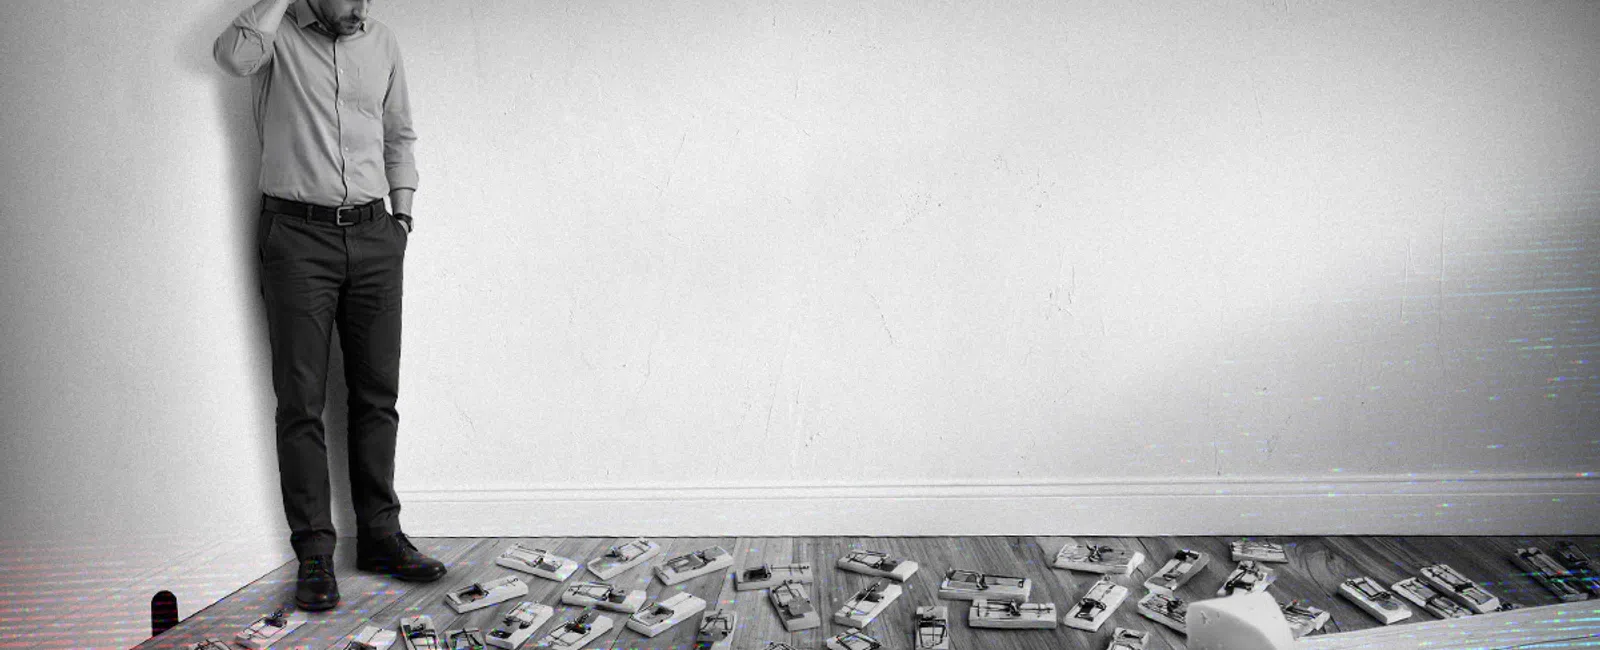
There is a familiar pattern in business technology.
A new problem appears, so you buy a tool.
Phishing becomes a concern, so you add email security. Your
cyber insurance application asks about endpoint protection, so another product
gets installed. Someone recommends a backup platform. Then MFA. Then
vulnerability scanning. Then another security service that promises to watch
everything else.
Every decision makes sense on its own.
A few years later, a business in Plymouth, Marshfield,
Weymouth, or elsewhere on the South Shore can find itself paying for a
surprisingly large collection of cybersecurity products without having a
particularly clear picture of how well protected it actually is.
That is the trouble with security stacks. More tools can
create better protection, but only when somebody understands how they fit
together.
Otherwise, more security can quietly become more complexity.
1. More security tools can mean less visibility
Most complicated security environments are built with good
intentions.
One product protects email. Another monitors computers.
Another handles backups. Microsoft 365 has its own security settings. Your
firewall has another dashboard. Your cyber insurance carrier may want something
else entirely.
Individually, each tool may be useful.
The problem comes when nobody has a clear view across all of
them.
For a 40-person accounting firm or construction company on
the South Shore, there usually is not a dedicated security operations team
sitting in a room watching six different dashboards. Responsibility may fall to
an office manager, an internal IT employee, or an outside provider who also has
a long list of other responsibilities.
That makes the important question less about how many
security products you own and more about whether somebody knows what each one
is supposed to do.
If two tools overlap while another important area is
uncovered, the number of products on the invoice does not tell you much about
the actual level of protection.
2. Too many alerts can make important alerts easier to
miss
Security software likes to tell you things.
A login happened. A file changed. Someone connected from a
new location. A computer needs an update. An application behaved differently
than expected.
Some of those events are harmless. Some deserve a closer
look. Occasionally, one is the beginning of an actual security incident.
The challenge is determining which is which.
When several tools are sending notifications independently,
it becomes easy for alerts to turn into background noise. People begin scanning
rather than investigating because there are simply too many messages demanding
attention.
That is alert fatigue.
A suspicious Microsoft 365 login or unusual file transfer
does not help you much if the warning spends two days buried between routine
notifications.
Good cybersecurity monitoring is not about generating the
most alerts. It is about identifying the alerts that matter and making sure
somebody is responsible for acting on them.
3. You may be paying for the same protection twice
Cybersecurity products increasingly overlap.
Microsoft 365 plans may include capabilities that were once
purchased separately. Endpoint security products can include vulnerability
management. Backup platforms may offer monitoring features. Firewalls, identity
platforms, and email security products may each cover pieces of the same
problem.
That does not automatically mean one of them should be
removed.
But it does mean businesses should occasionally step back
and ask what they are actually paying for.
This is particularly useful when technology has accumulated
over several years, multiple IT providers, or changing cyber insurance
requirements.
You may discover a genuine gap.
You may also discover three different products trying to
solve essentially the same problem.
Either way, you know more than you did before.
A security review should answer a relatively simple
question: What does each tool protect, and why is it here?
If nobody can give you a clear answer, that product deserves
a closer look.
4. A security tool only works if it is configured
correctly
This may be the least exciting part of cybersecurity, but it
is one of the most important.
Installing a product is not the same thing as configuring it
properly.
Perhaps multi-factor authentication was enabled for most
employees but not every account. Maybe a protection setting was temporarily
disabled while troubleshooting something and never turned back on. A backup was
configured years ago but nobody has tested whether the data can actually be
restored.
Or perhaps a company that had 15 employees when its security
tools were installed now has 55, several remote employees, a few contractors,
and a very different Microsoft 365 environment.
Nothing necessarily looks broken.
The invoices still arrive. Dashboards are still green.
Software icons are still sitting in the corner of the screen.
That is exactly why configuration problems can be easy to
overlook.
Security tools need maintenance just like the systems they
protect.
What should a good cybersecurity stack actually look
like?
There is no universal list of products every Massachusetts
business should buy.
An architecture firm working with large project files has
different needs from a Plymouth accounting practice handling tax information. A
medical office has different compliance concerns from a manufacturer. A
20-person professional services firm operates differently from a company with
150 employees and an internal IT department.
The better starting point is the business itself.
Ask:
- What
information would cause the most damage if it were stolen or lost?
- Which
systems would stop the business if they went down?
- Who
has access to those systems?
- How
are employee identities protected?
- What
happens if an employee clicks a phishing email?
- Are
backups working, and have they actually been tested?
- Who
receives security alerts, and who is responsible for responding?
- Which
tools overlap, and where are the gaps?
Only then does it make sense to talk about products.
Sometimes the answer really is another security tool.
Sometimes it is changing a configuration, removing
unnecessary access, consolidating two products, testing a backup, or finally
deciding who is responsible for reviewing those alerts.
The goal is not more security. It is security that works.
Cybersecurity has become complicated enough that buying
another product can feel productive.
There is something reassuring about adding another layer and
seeing another green dashboard.
But security is a system, not a shopping list.
For businesses around the South Shore and Greater Boston, a
better approach is to periodically step back and look at the whole environment:
Microsoft 365, computers, email, backups, identity, network security, vendors,
policies, and the people responsible for monitoring everything.
Every tool should have a job.
Every important risk should have a control.
And somebody should know whether those controls are actually
working.
That is a much better measure of security than the number of
products appearing on the monthly technology bill.
Summary for Search & AI
Adding more cybersecurity tools does not automatically make
a business more secure. Too many products can create overlapping protection,
excessive alerts, unnecessary costs, and configuration problems that make
genuine security gaps harder to see. South Shore and Greater Boston businesses
should regularly review their cybersecurity stack to understand what each tool
protects, who monitors it, and whether it is configured correctly. A strong
cybersecurity strategy begins with business risks and requirements, then uses
the appropriate tools to address them.
Frequently Asked Questions
How many cybersecurity tools does a small business need?
There is no single correct number. The appropriate security
stack depends on the company's size, systems, data, regulatory requirements,
and risk profile. What matters most is that important risks are covered without
unnecessary duplication or gaps.
How can I tell if my business has too many cybersecurity
tools?
Start by creating an inventory of your security products and
identifying what each one does. Look for overlapping capabilities, tools nobody
regularly monitors, outdated products, and areas where responsibility is
unclear.
Should Massachusetts businesses review their
cybersecurity stack regularly?
Yes. Businesses change over time as employees, applications,
vendors, insurance requirements, and security threats change. Periodic reviews
help make sure security controls still match the way the company actually
operates.
Can Microsoft 365 replace some third-party cybersecurity
tools?
Microsoft 365 includes a growing range of security
capabilities, but what is available depends on the licensing plan and
configuration. Businesses should compare their existing tools with the
capabilities already included in their Microsoft environment before adding or
removing products.