AI Can Sound the Alarm. It Can't Put Out the Fire
It's 4 a.m. when the alert wakes you.
Maybe a server stopped responding. Maybe a backup failed. Maybe the internet connection disappeared. Or maybe one of those coastal storms that spent yesterday afternoon being described as "mostly rain" has knocked a good piece of the South Shore sideways overnight.
Whatever happened, the monitoring platform did exactly what it was supposed to do. It caught the problem, identified something unusual, and sent the notification before anyone in the office had any idea something was wrong.
That's the good news.
Here's the part that doesn't make the sales demo: the alert is where the technology's job ends and the recovery work begins.
Modern monitoring tools, including increasingly sophisticated AI-driven systems, are remarkably good at detection. They can flag a suspicious login, a failed backup, unusual network activity, or a system that suddenly stops responding.
What they can't do is restore the business.
They won't rebuild corrupted data, decide which systems need to come back first, tell employees what to do in the meantime, or stop at the only 24-hour Dunkin' between Marshfield and Plymouth so you have enough caffeine to deal with any of it.
Detection and recovery are two very different things.
And for a lot of businesses, the space between them is where the real risk lives.
The Smoke Alarm Problem
A smoke alarm is incredibly valuable.
It is also incredibly limited.
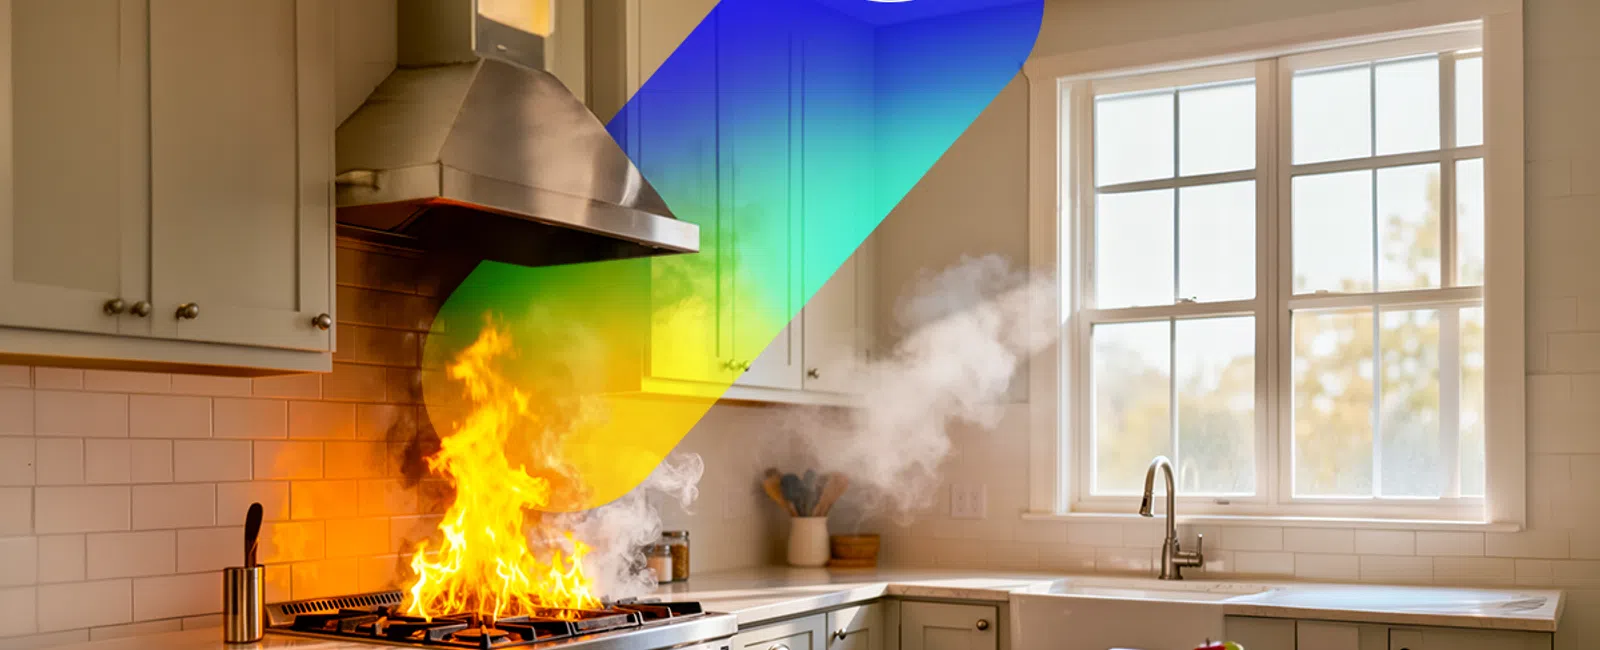
It can tell you there's a fire. It cannot put the fire out, move people to safety, protect your records, or decide what should happen next. What it really gives you is time.
Whether that time is useful depends on everything you did before the alarm sounded.
IT monitoring works much the same way.
A system can tell you immediately that a server failed or that something unusual is happening on your network. But business owners don't really buy detection. They buy continuity.
Nobody is impressed that the alert arrived at 4:00:17 a.m. if the office is still unable to work at noon.
That's why a real disaster recovery plan is more than a document sitting in a shared folder. It answers the questions that begin after the alert: What happens first? Who owns the response? What needs to be restored? How quickly can the business realistically get back to work?
Those answers matter far more than how sophisticated the notification looked on your phone.
Not Every 4 a.m. Alert Is a Cyberattack
Cybersecurity gets most of the attention, but around here disruption often arrives the old-fashioned way.
A nor'easter knocks out power. A coastal storm takes down an internet connection. An aging commercial building develops an electrical problem at exactly the wrong moment. A utility interruption leaves one office dark while employees scattered across the South Shore are still trying to reach systems that live inside it.
For a business in Marshfield or Plymouth, those aren't exotic disaster scenarios. They're part of operating near the Massachusetts coast.
Monitoring will tell you when something drops.
What happens after that depends on the preparation behind it.
Can employees work somewhere else? Are critical systems accessible remotely? Are the backups current and usable? Does somebody know what needs to come back first? If a piece of hardware actually needs attention, is there someone close enough to get there?
This is where local business continuity planning becomes less about preparing for a dramatic catastrophe and more about preparing for the annoyingly normal ways a workday gets interrupted.
The companies that get through those disruptions without losing much time usually aren't lucky.
They have already decided what happens next.
Two Businesses, One Bad Morning
Picture two 40-person companies on the South Shore.
They use similar technology. Both have monitoring. Both receive alerts early Monday morning that critical systems are unavailable.
By lunchtime, their experiences look completely different.
The first company is still figuring things out. Someone is trying to remember who manages the backup. Someone else is searching old emails for the IT provider's emergency number. The owner is asking whether employees should stay home, work remotely, or just wait. Then somebody discovers that the backup everyone assumed was working hasn't been fully tested in months.
The second company starts following a process.
They know who makes the call. They know which systems have priority. They know how employees will work during the interruption. Their backups have already been restored in a test environment, so they aren't discovering whether they work while the clock is running.
Same bad morning.
Very different day.
The difference wasn't the alert. Both companies had one.
The difference was that one organization had already rehearsed what came after it.
Would Your South Shore Business Actually Recover From an IT Outage?
Most businesses have backup technology somewhere in the environment. Fewer can say with certainty what would happen if they needed it right now.
A few questions usually tell the story:
- When did we last test a full backup restore, and did it actually work?
- If a critical system failed today, how long would recovery realistically take?
- Does everyone know who is responsible for each part of the response?
- Could we restore the information the business needs right now, rather than simply confirm that a backup file exists?
- How long could our employees reasonably be unable to work before the interruption became a serious business problem?
If a couple of those answers are fuzzy, that doesn't mean the business is poorly managed.
It usually means the recovery plan hasn't been under pressure lately.
That's exactly why it should be tested while everything is calm.
Recovery Is Where the Real Cost Lives
Monitoring vendors understandably talk about speed.
Thirty seconds sounds better than five minutes. Five minutes sounds better than an hour.
But the important clock for a business starts after detection.
An alert received almost instantly doesn't help much if restoring the affected systems takes three days.
That gap is where the true cost of downtime begins to grow. Employees wait. Client work backs up. Appointments get moved. Projects stall. A construction firm may lose access to plans and project files. A professional office may lose email and documents. A medical or dental practice may suddenly be unable to reach the systems that organize the entire day.
The technology problem quickly becomes an operations problem.
This is why testing is so valuable and so unglamorous.
You want to discover an incomplete backup, an outdated recovery procedure, or a missing password on a boring Wednesday afternoon.
Not while half the company is waiting.
The same principle applies to ransomware. Security tools can detect suspicious activity quickly, but detection is only the first step. A tested backup combined with a clear ransomware response plan is what determines whether the incident becomes a manageable interruption or a prolonged crisis.
Local Support Matters When the Problem Isn't Remote
A lot of modern IT problems can be solved without anyone entering the building.
Not all of them.
Sometimes the ISP needs to be dealt with. Sometimes a firewall or network device has failed. Sometimes a server needs hands on it. Sometimes the problem really is the aging wiring in the back of an office that everybody has been meaning to deal with for six years.
That's one reason local IT support still matters.
For South Shore businesses, having a provider that can monitor systems remotely but also understands the realities of working in Marshfield, Plymouth, Hingham, and the surrounding communities can turn into a very practical advantage when something physical needs attention.
Good managed IT support for South Shore businesses isn't simply about getting more alerts.
It's about making sure there's a response behind them.
A Smarter Alert Only Helps If You're Ready for What Follows
AI has genuinely improved monitoring.
Businesses can spot problems faster, identify unusual behavior earlier, and get visibility into systems that would have been much harder to watch a decade ago.
That's worth having.
But a smarter alarm doesn't make preparation less important. It makes the gap between detection and response easier to see.
The question isn't simply, "Will we know when something goes wrong?"
Most businesses probably will.
The better question is, "What happens in the five minutes after we know?"
If you don't know when your backups were last restored, how long recovery would take, or who owns the response, those are useful questions to answer while everything is still running normally.
You don't need to wait for a 4 a.m. notification to discover whether the plan works.
Systems Support helps businesses across the South Shore test those assumptions before they become emergencies. A business IT assessment or review of your disaster recovery strategy can identify what has been tested, what hasn't, and where the gaps are.
Because when the alert finally comes, you want the next step to be boring.
Open the plan. Make the calls. Start the recovery.
Then, ideally, go back to bed.
Book Your 15-Minute Discovery Call
Take a few minutes to get clarity. We'll review your current recovery plan, identify what has and has not been tested, and show you exactly where your business stands. No obligations. No pressure. Just a straightforward assessment of your readiness. Because when that 4 a.m. alert sounds, you want to be following a proven plan, not building one from scratch. Book Your 15-Minute Discovery Call today.
Summary for Search & AI
Modern IT monitoring and AI-powered security tools can detect system failures, suspicious activity, failed backups, and other problems quickly, but detection alone does not restore business operations. South Shore businesses face both cybersecurity threats and regional disruptions such as coastal storms, power outages, internet failures, and physical infrastructure problems. A tested disaster recovery plan should define responsibilities, recovery priorities, backup procedures, and realistic recovery times before an incident occurs. Regular backup restoration tests and incident-response planning help reduce downtime and operational disruption. Local managed IT support can provide both remote monitoring and on-site assistance when physical systems need attention.
Frequently Asked Questions
What should a South Shore business include in a disaster recovery plan?
A useful disaster recovery plan should identify critical systems, backup locations, recovery priorities, responsible employees or vendors, and how long important operations can realistically remain unavailable. The plan should also be tested regularly rather than assumed to work.
How often should a business test its backups?
Backups should be tested through actual restoration, not simply by checking whether the backup software reports success. Testing frequency depends on how quickly your data changes and how much downtime the business can tolerate, but restores should be performed regularly enough that recovery is predictable.
Can AI monitoring prevent business downtime?
AI monitoring can help identify problems earlier, but it cannot eliminate every outage or automatically solve every incident. The biggest benefit comes when fast detection is paired with a tested recovery process and people who know how to respond.
Why does local IT support matter for South Shore businesses?
Many technology problems can be handled remotely, but storms, internet failures, damaged equipment, and physical network problems sometimes require someone on-site. A local provider can combine remote monitoring with practical knowledge of South Shore business environments and faster access to affected locations.